Human-in-the-Loop Governance
“Human expertise, backed by AI” is a framework here, not a tagline. Our human-in-the-loop AI model defines which actions AI can execute, which require human approval, and how each action is recorded for review.
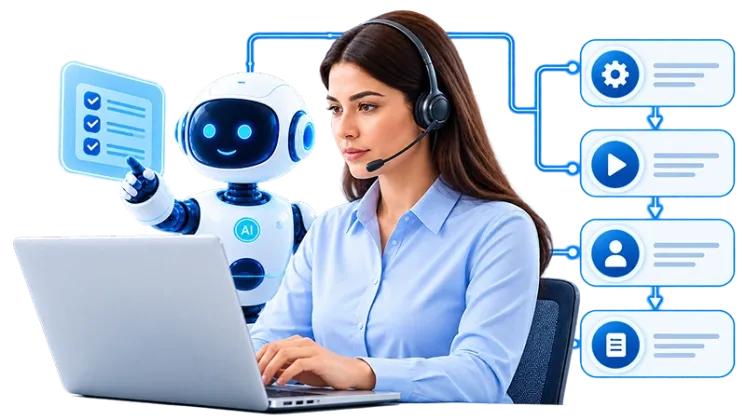
For compliance, operations, and vendor-risk teams, the key requirement is control: what AI is authorized to do, where human approval is mandatory, and what evidence is available for review.
The table below defines that boundary, set during onboarding and enforced within the workflow through agreed governance rules rather than individual agent discretion.

AI acts autonomously
- Order status and account lookups
- Intent-based routing decisions
- Generation of suggested agent responses
- Real-time sentiment flagging
- Structured back-office tasks (refund initiation, data entry)
A human reviews or acts
- Anything outside the pre-approved action set
- Escalations and exceptions
- QA findings requiring judgment, exception handling, or further review
- Compliance-sensitive account changes
- Final sign-off before a suggested response reaches a customer
Pre-approved actions can proceed automatically. Higher-risk, exceptional, or compliance-sensitive actions move to human review or approval. Every action follows the approved path: execute and log when it falls within scope, or escalate for human approval, modification, or rejection when it falls outside the defined boundary.

How the boundary is set, not just stated
The specific list of what counts as a pre-approved, low-risk actions is defined during onboarding, based on your risk tolerance and regulatory context. Approval boundaries are configured to your workflow, operating environment, and internal control requirements. Anything added to the autonomous-action list goes through a review before go-live, and the list is revisited as the engagement matures. The result is AI behavior that stays predictable rather than left to individual interpretation in the moment.
What the audit trail actually contains
Every AI-initiated action is logged as it happens, whether it clears automatically or moves through the AI agent approval workflow to a person, capturing what it was, when it happened, which approved category it fell under, and, where relevant, what triggered escalation. That's what lets your compliance or vendor-risk team trace a specific AI action back to the interaction it came from and the rule under which it was permitted, not just a description of the model.

Ask us where the line sits for your use case
We can review your proposed automation scope, approval requirements, exception scenarios, and audit needs against the human-in-the-loop governance model.
Ask us where the line sits for your use case
We can review your proposed automation scope, approval requirements, exception scenarios, and audit needs against the human-in-the-loop governance model.
Schedule a Free Consultation
FAQ
Frequently asked Questions
Yes. Tightening it doesn't require rebuilding the workflow: flag the categories you want pulled back to human review, and we update the approval rules in your AI agent oversight platform.
Anything outside the pre-approved list: exceptions, compliance-sensitive account changes, and any suggested response before it reaches a customer. Nothing consequential moves without a person.
Any addition to the autonomous-action list is reviewed against your risk tolerance and regulatory context before it goes live, not after, preventing the boundary from expanding without a check.
Every suggested response gets human sign-off before reaching a customer as part of our AI agent approval workflow. A disputed action is reviewed against the same 100% QA scoring applied to every interaction.
Timelines vary by regulatory complexity, but most clients have a documented boundary in place within the first two weeks of onboarding, before go-live.
Yes. The log is structured for reconciliation against specific interactions, so your compliance team can request exports directly from our AI oversight and audit trail platform on the cadence your review process requires.
Not automatically. The action categories stay the same as volume grows within your human-in-the-loop workflow automation; what changes is escalation frequency, which we review with you periodically to confirm the boundary still fits.